Recent Posts

Week 32 – N-able N-central – Take Control Taken Over

03-09 Aug 2026 CVE-2026-18577 is a critical authentication bypass vulnerability affecting N-able N-central. Due to an incomplete patch, attackers can gain administrative access, abuse the built-in Take Control feature, and pivot to managed endpoints. Read White Hat IT Security’s analysis to understand the attack chain, 

Applications now closed for CyAN’s Mentorship Programme, Autumn 2026

Applications now closed for CyAN’s Mentorship Programme, Autumn 2026

Note: applications are now closed CyAN’s mentorship programme is back for its autumn 2026 cohort, running from mid-September to mid-December. The programme is free and volunteer-led. It pairs people building a career in cybersecurity, or a related field, with experienced CyAN members for three months 

Cyber (In)Security – Issue #207

The fortnightly newsletter of the Cybersecurity Advisors Network (CyAN) — Issue #207, 4 August 2026. This issue leads with governance and civil-society resilience, plus the latest from our members and partners. Downloadable full PDF at the bottom of this post. In this issue Are you 

CyAN Signs Protect.ngo / ICSC Call to Protect Civil Society Organisations

CyAN Signs Protect.ngo / ICSC Call to Protect Civil Society Organisations

CyAN supports the call to strengthen organisations protecting societal resilience.

Week 31 – CertiGhost: The Certificate That Shouldn’t Exist

27 July – 02 Aug 2026 This week’s CVE of the Week is CVE-2026-54121, also known as CertiGhost, a critical vulnerability affecting Microsoft Active Directory Certificate Services (AD CS). The flaw allows a low-privileged authenticated domain user to obtain a certificate for a Domain Controller, 

Governing Security When the CISO Advises but Doesn’t Command – by Kamran Israr Mirza (Kim)

Governing Security When the CISO Advises but Doesn’t Command – by Kamran Israr Mirza (Kim)

When the SOC reports to the CTO and the CISO’s role is advisory only, accountability and authority quietly split apart; this white paper makes the case for elevating the CISO’s reporting line to the CEO or Board and giving the function its own budget.

Week 30 – A PDF Extension with a WhatsApp Obsession

20 -26 July 2026 In this week’s CVE of the Week, we’re examining a recently patched vulnerability chain in the Adobe Acrobat PDF Chrome extension, which is used by more than 314 million users worldwide. Tracked as CVE-2026-48294 (CVSS score: 8.2) and dubbed HermeticReader by 

Cyber (In)Security – Issue #206

In this issue: Want your content featured? Tag @Cybersecurity Advisors Network in your LinkedIn post — articles, presentations, awards, new roles, or external events — and we’ll pick it up for the next issue.

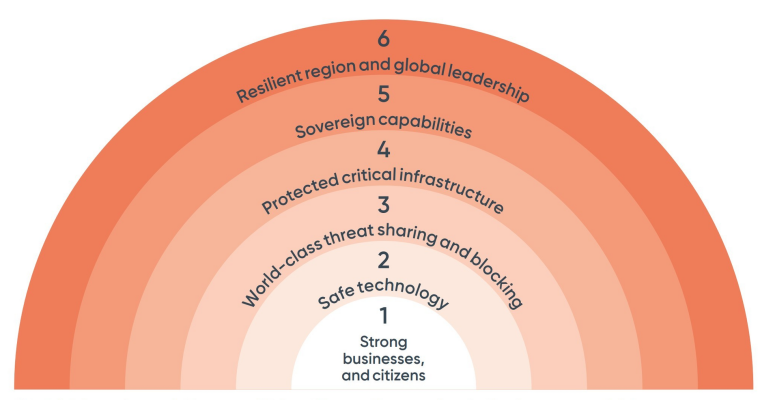
Australia’s Horizon Cyber Security Initiative: What it Means for Industry – by David Gaul

Australia’s Horizon Cyber Security Initiative: What it Means for Industry – by David Gaul

Few people ask about the implications of Australia’s cyber security reform on businesses – this paper addresses important aspects of the initiative.

Cyber Risk Is in the Boardroom. Are Boards Ready to Govern It? – By Sanchay Joshi

Cyber Risk Is in the Boardroom. Are Boards Ready to Govern It? – By Sanchay Joshi

Sanchay Joshi explores improved approaches for boards to ensure oversight of cybersecurity and resilience, and how this makes organisations stronger