Recent Posts

Week 41 – The Weight of a Secret: Atlassian’s Critical File Read Flaw

05 – 11 Oct 2026 Read-only access. Full admin privileges? Our latest CVE of the Week explores CVE-2026-21589, a critical vulnerability affecting self-hosted Atlassian products, including Jira, Confluence, and Bitbucket. Attackers can access sensitive configuration files without authentication – potentially turning a simple file-read flaw …
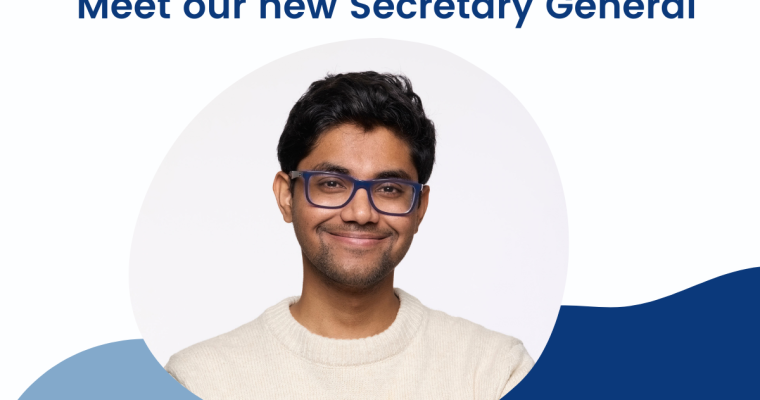
Meet our new Secretary General

Meet our new Secretary General

We are pleased to announce the appointment of Aahil Sheikh as our new Secretary General. As CyAN aims to strengthen and protect the global digital society and the information economy, Aahil brings his experience in digital policy across the EMEA and APAC regions. He has …

Week 40 – Code injection: Sneaking in

28 Sept – 04 Oct 2026 A high-severity vulnerability in Microsoft SharePoint Server has recently drawn attention. CVE-2026-65660 is a CWE-94 code injection vulnerability that can allow an authenticated attacker to execute arbitrary code on an affected SharePoint Server. The vulnerability has a CVSS 3.1 …

Cyber (In)Security – Issue #210

#CyAN #CRA #VARA #mentorship #trustandsafety

Week 39 – Check Point Under Attack: Critical Zero-Day Exploited in the Wild

21 – 27 Sept 2026 What happens when the security infrastructure itself becomes the target? This week’s CVE of The Week covers CVE-2026-93616, a critical Check Point zero-day vulnerability with a CVSS score of 9.8 — exploited in targeted attacks before a patch was available. …

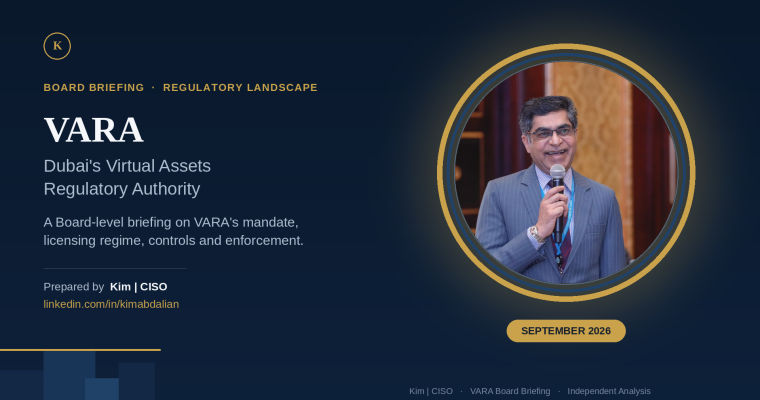
VARA: Dubai’s Virtual Assets Regulatory Authority

VARA: Dubai’s Virtual Assets Regulatory Authority

A board-level briefing on Dubai’s VARA regime, covering licensing, AML/CFT controls,enforcement actions and the compliance gaps that ISO 27001,

Week 38 – GitLab Under Attack: Critical Arbitrary File Read Vulnerability

14 – 20 Sept 2026 What if an unauthenticated user could read your sensitive data from the GitLab server? This week’s CVE of the Week highlights CVE-2026-85706 in GitLab – a critical CVSS 10.0 flaw that could allow unauthenticated attackers to read arbitrary files from …

Week 37 – SAP Attack: When the Buffer Says “No More”

07 – 12 Sept 2026 A critical CVSS 10.0 vulnerability puts thousands of Internet-facing SAP systems potentially at risk. Our latest CVE of the Week covers CVE-2026-44756, a buffer overflow vulnerability in the SAP Kernel that could enable remote attackers to execute code with administrative …

Cyber (In)Security – Issue #209

Cyber (In)Security – Issue #209

CyAN’s latest fortnightly digest is out – #209

The CyAN Mentorship Programme Returns for Autumn 2026

The CyAN Mentorship Programme Returns for Autumn 2026

Announcing the CyAN fall 2026 mentorship programme