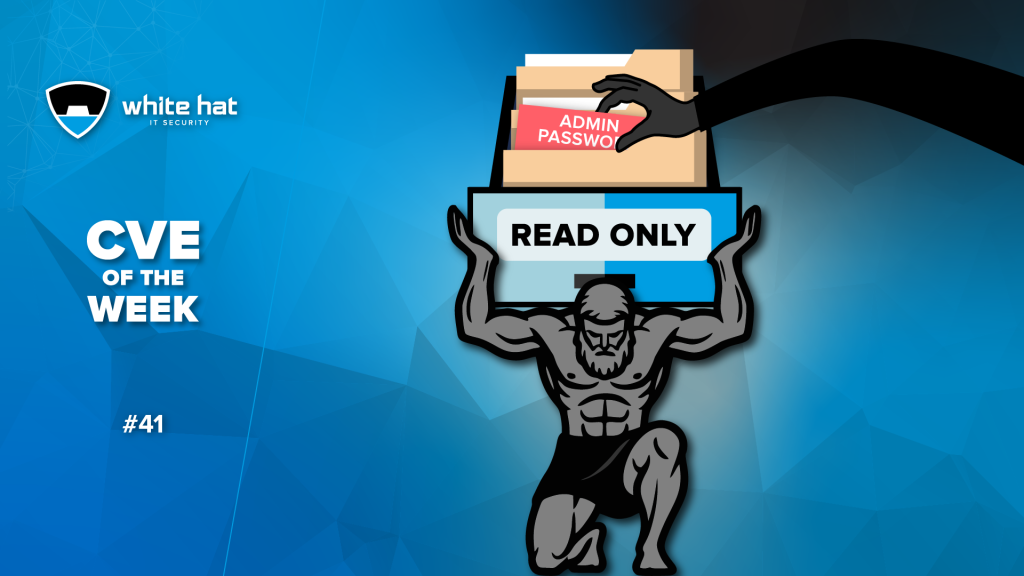
Week 41 – The Weight of a Secret: Atlassian’s Critical File Read Flaw
05 – 11 Oct 2026
Read-only access. Full admin privileges?
Our latest CVE of the Week explores CVE-2026-21589, a critical vulnerability affecting self-hosted Atlassian products, including Jira, Confluence, and Bitbucket.
Attackers can access sensitive configuration files without authentication – potentially turning a simple file-read flaw into a complete administrative takeover.
Atlas may carry the weight, but can he keep the secrets?
Read our latest article on the White Hat blog to discover how the attack works and why immediate patching matters.
White Hat IT Security is a Europe-based Managed Security Services Provider (MSSP) and proud Microsoft Solution Partner. Its Microsoft-verified managed security solutions (MXDR) reflect their deep expertise and commitment to excellence in cybersecurity. The company was awarded the Partner of the Year Hungary Award by Microsoft in 2024 and 2025.
With the largest incident response capacity in the CEE region, they’re trusted by organizations to deliver fast, effective, and proactive protection. Their portfolio includes penetration testing, vulnerability assessments, managed Cyber Threat Intelligence, as well as Governance, Risk and Compliance (GRC) consulting and specialized security training.
They are committed to supporting professional initiatives that aim to raise cybersecurity awareness and maturity—both for individuals and organizations. They regularly contribute to the community through knowledge sharing, education, and outreach, helping to build a safer digital future for all.